01
HIPAA Security Rule Alignment
Support administrative, technical, and operational safeguard expectations through practical security program improvements.
DBT helps healthcare providers, clinics, specialty practices, and healthcare-adjacent organizations strengthen HIPAA-aligned security controls, identity security, incident readiness, and operational resilience.
Healthcare organizations face ransomware, phishing, business email compromise, identity compromise, vendor risk, cyber insurance pressure, and audit expectations. DBT helps Kentucky healthcare organizations connect HIPAA readiness with practical cybersecurity controls, evidence collection, and operational risk reduction.
DBT helps healthcare organizations improve the safeguards, monitoring, access controls, and response capabilities that support HIPAA Security Rule readiness.
Support administrative, technical, and operational safeguard expectations through practical security program improvements.
Identify cybersecurity and operational risk areas that may affect ePHI confidentiality, integrity, and availability.
Strengthen authentication, unique user access, remote access, privileged accounts, and access review practices.
Improve visibility into user activity, security events, suspicious access, and evidence needed for investigations.
Identify and prioritize exposed systems, missing patches, unsupported software, and configuration weaknesses.
Prepare for ransomware, unauthorized access, suspected breach events, business associate notifications, and recovery coordination.
Support workforce security expectations with phishing awareness, user training, and practical security reinforcement.
Improve documentation, reporting, control mapping, and audit support for HIPAA-aligned cybersecurity activities.
DBT helps healthcare organizations improve cybersecurity in ways that support clinical workflows, remote access, administrative operations, vendor dependencies, and leadership reporting. The goal is practical security improvement, not checkbox-only compliance.
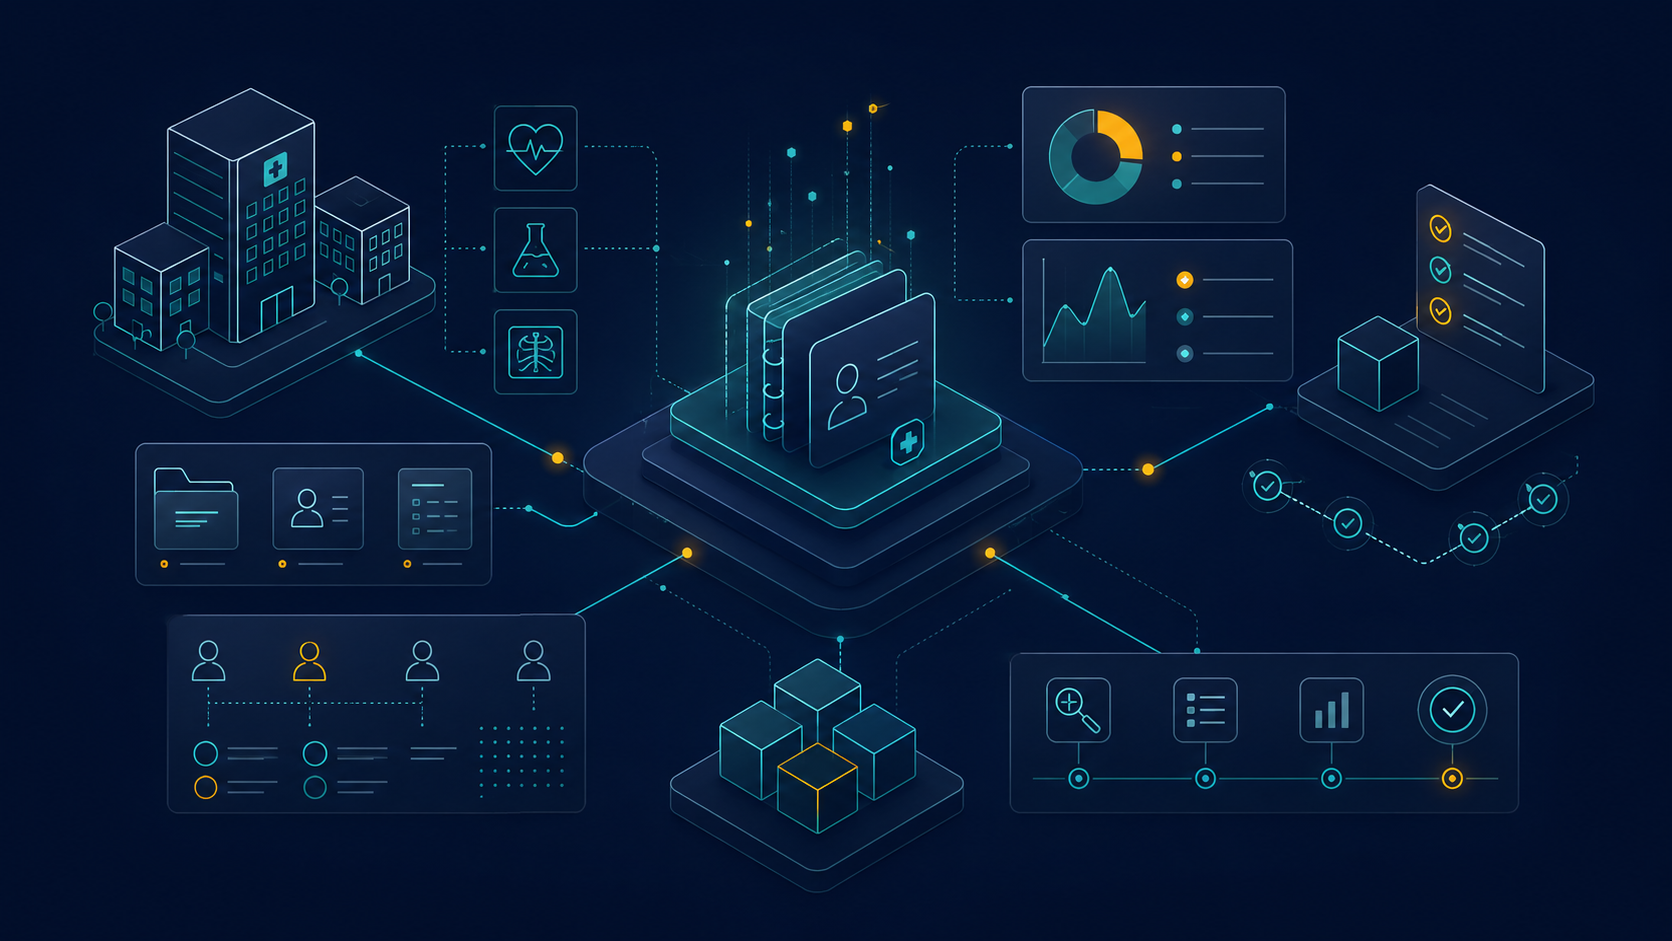
DBT maintains HIPAA-focused resources covering safeguards, access control, audit logs, contingency planning, breach response, incident response, workforce training, business associates, and healthcare cybersecurity risk assessment.

Improve safeguards, access controls, monitoring, risk visibility, and incident readiness for healthcare environments.
Strengthen administrative, technical, and operational safeguards that support HIPAA Security Rule readiness.
Improve MFA, access policies, privileged account controls, and identity visibility for users and administrators.
Support documentation, monitoring, reporting, and evidence collection for internal reviews, audits, and investigations.
Prepare for ransomware, unauthorized access, suspected breach events, and recovery coordination.
Focus limited resources on the security gaps most likely to affect ePHI, continuity, and compliance posture.
Align cybersecurity improvements with healthcare operations, business associates, workforce needs, and regulatory expectations.
Related HIPAA Resources
Explore DBT resources on HIPAA Security Rule readiness, healthcare risk assessments, access control, audit logging, incident response, contingency planning, and business associate risk.
As DBT builds out formal case studies, these anonymized outcome examples preview the types of security, identity, compliance, and operational improvements the site should route visitors toward.
“DBT helped us modernize authentication, improve visibility, and strengthen our security posture without disrupting operations.”
“Their cybersecurity-first mindset is very different from a traditional MSP. The focus on operational risk and resilience has been invaluable.”
“DBT helped align our identity and compliance initiatives while improving the user experience. Their strategic guidance has been excellent.”
DBT’s Security Readiness Assessment helps identify gaps across cybersecurity operations, identity, compliance, infrastructure, monitoring, and resilience so your team can prioritize practical improvements.